TeamPCP strikes again - telnyx 4.87.1 and 4.87.2 on PyPI…

0 reactions
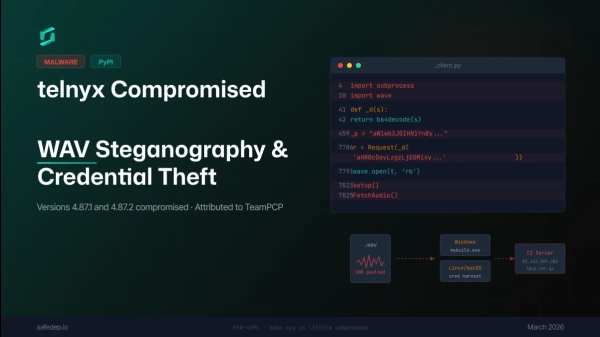
TeamPCP strikes again - telnyx 4.87.1 and 4.87.2 on PyPI are malicious
Same actor, same RSA key, same `tpcp.tar.gz` exfiltration header as the litellm compromise last week.
This time they injected into `telnyx/_client.py` \- triggers on `import telnyx`, no user interaction needed. New trick: payload is hidden inside WAV audio files using steganography to bypass network inspection.
On Linux/macOS: steals credentials, encrypts with AES-256 + RSA-4096, exfiltrates to their C2. On Windows: drops a persistent binary in the Startup folder named `msbuild.exe`.
They even pushed a quick 4.87.2 bugfix to fix a casing error that was breaking the Windows path. These folks are paying attention.
Pin to `telnyx==4.87.0`. Rotate creds if you installed either version.
Full analysis with IoCs here https://safedep.io/malicious-telnyx-pypi-compromise/
#technology #programming #dev


| 3,000 mlx | |
| 4 | |
| 0 |