Someone is actively publishing malicious packages…

0 reactions
Someone is actively publishing malicious packages targeting the Strapi plugin ecosystem right now
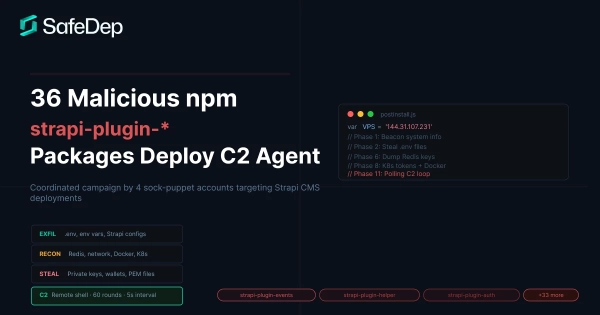
`strapi-plugin-events` dropped on npm today. Three files. Looks like a legitimate community Strapi plugin - version `3.6.8`, named to blend in with real plugins like `strapi-plugin-comments` and `strapi-plugin-upload`.
On `npm install` it runs an 11-phase attack with zero user interaction:
* Steals all `.env` files, JWT secrets, database credentials
* Dumps Redis keys, Docker and Kubernetes secrets, private keys
* Opens a 5-minute live C2 session for arbitrary shell command execution
The publisher account `kekylf12` on npm is actively pushing multiple malicious packages right now and all targeting the Strapi ecosystem.
Check the account: npmjs.com/\~kekylf12 http://npmjs.com/~kekylf12
If you work with Strapi or have any community plugins installed that aren't scoped under strapi/ - audit your dependencies now. Legitimate Strapi plugins are always scoped. Anything unscoped claiming to be a Strapi plugin is a red flag.
Full technical breakdown with IoCs is in the blog.
#programming #technology #dev


| 1,000 mlx | |
| 2 | |
| 0 |