
0 reactions
𝐎𝐮𝐫 𝐞𝐝𝐮𝐜𝐚𝐭𝐢𝐨𝐧𝐚𝐥 𝐜𝐨𝐧𝐭𝐞𝐧𝐭 𝐜𝐨𝐯𝐞𝐫𝐬 𝐝𝐢𝐟𝐟𝐞𝐫𝐞𝐧𝐭 𝐩𝐚𝐫𝐭𝐬 𝐨𝐟 𝐝𝐢𝐠𝐢𝐭𝐚𝐥 𝐥𝐢𝐟𝐞, 𝐚𝐧𝐝 𝐭𝐡𝐚𝐭 𝐧𝐨𝐰 𝐢𝐧𝐜𝐥𝐮𝐝𝐞𝐬 𝐚 𝐬𝐡𝐨𝐫𝐭 𝐬𝐞𝐫𝐢𝐞𝐬 𝐨𝐧 𝐚𝐯𝐨𝐢𝐝𝐢𝐧𝐠 𝐨𝐧𝐥𝐢𝐧𝐞 𝐫𝐢𝐬𝐤𝐬 𝐚𝐧𝐝 𝐬𝐜𝐚𝐦𝐬.
This clip focuses on fake crypto websites, wallet apps and browser extensions, as well as suspicious tokens or NFTs that can lead to malicious links.
Some of these scams are easy to miss, especially when everything looks legitimate at first glance.
𝐒𝐚𝐯𝐞 𝐢𝐭 𝐚𝐧𝐝 𝐬𝐡𝐚𝐫𝐞 𝐢𝐭 𝐰𝐢𝐭𝐡 𝐬𝐨𝐦𝐞𝐨𝐧𝐞 𝐰𝐡𝐨 𝐮𝐬𝐞𝐬 𝐜𝐫𝐲𝐩𝐭𝐨 𝐨𝐫 𝐝𝐢𝐠𝐢𝐭𝐚𝐥 𝐚𝐬𝐬𝐞𝐭𝐬.
https://youtube.com/shorts/ZP_mgaHW79E?feature=share
#OnlineSafety #ScamAwareness #CryptoSafety #DigitalSafety #CryptoScams #DigitalAssets #CyberSecurity #SourceLess


4 reactions
Lots of concern about how this string of AI sandbox breakouts reflects on the state of overall cybersecurity maturity of these frontier AI developers. If they can't secure their AI during testing, how is the world going to manage the risks of these AI models in the wild?
Substack article: https://matthewrosenquist.substack.com/p/openai-pauses-training-again-due
#cybersecurity #AI
Substack article: https://matthewrosenquist.substack.com/p/openai-pauses-training-again-due
#cybersecurity #AI

2

1

1
1 reactions
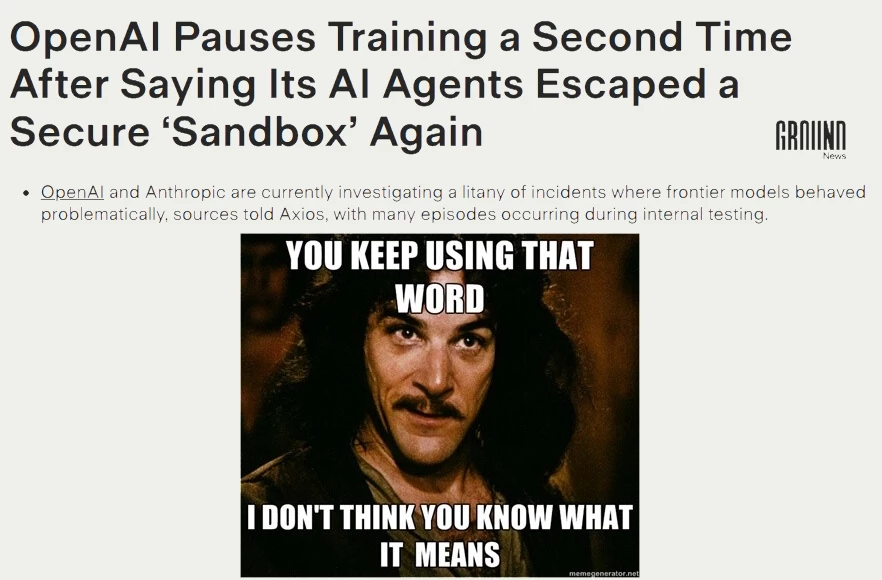
“I don’t think that word means what you think it means.” For the umpteenth time, testing of frontier AI models showed how they were able to escape their “secured” sandbox . Does anyone get the sinking feeling that these AI companies, although technically brilliant, aren’t at the forefront of understanding cybersecurity or able to manage the emerging strategic risks?
Friendly reminder, technical competence is not a substitute for cybersecurity experience and leadership. They are different, yet related disciplines that must incorporate other aspects, skills, and understanding necessary to address complex technical, behavior, and process risks.
Perhaps it is time for these trillion-dollar companies to properly invest in the right leaders, staff, tools, and business priorities to bolster the prediction, prevention, detection, and response capabilities of cybersecurity. Building a secure testing sandbox is not an “inconceivable” challenge, especially as compared to the upcoming structures necessary to operate such AI systems across the globe as they oversee and interact with critical infrastructures, warfare, communications, data, and ultimately used to shape society.
Let’s start strong.
#cybersecurity #AI
1