axios 1.14.1 and 0.30.4 on npm are compromised…
0 reactions
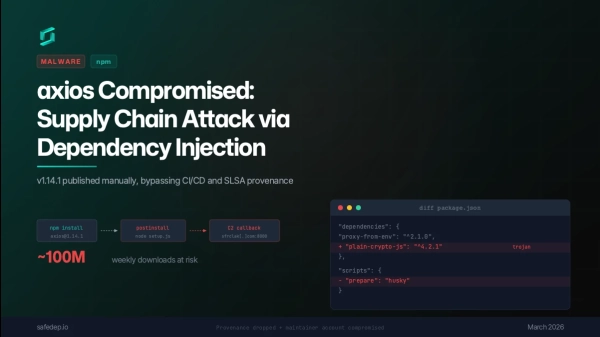
axios 1.14.1 and 0.30.4 on npm are compromised - dependency injection via stolen maintainer account
Two versions of axios were published today through what appears to be a compromised maintainer account. No GitHub tag exists for either version. SLSA provenance attestations present in 1.14.0 are completely absent. Publisher email switched from the CI-linked address to a Proton Mail account( classic account takeover signal).
If your project floats on `^1.14.0` or `^0.30.0` you've likely already pulled this.
IoCs, payload analysis and full breakdown is in the blog.
#technology #programming #dev #js


| 3,000 mlx | |
| 3 | |
| 0 |